
 EuroCloud
certification scheme
Trusted and audited cloud services
European quality scheme for global usage
Checklists for provider transparency and tender support. Assessment tools for quality checks, gap analysis and audit purposes.
Our online self-assessment is being rebuilt. To start an assessment in the meantime, contact office@staraudit.org.


Get to know us better
Download the StarAudit catalogue and get a more in-depth look at what an assessment covers — the full criteria catalogue and a compact overview.

Latest News
All news →
Deleting an Account Is Not the Same as Deleting Personal Data: Lessons from EU GDPR Enforcement

Bidding on Sensitive Data: Norway's Record Fine Against Xandr
The Norwegian Data Protection Authority (Nw.: "Datatilsynet") has, in decision 20/03541-37, imposed the largest fine in its history: NOK 92 million (approximately EUR 8.6 million) against Microsoft-owned AdTech company Xandr Inc. for unlawfully processing and sharing special categories of personal data about Grindr users through real-time bidding (RTB). The decision and the Authority's parallel public guidance illustrate its approach to programmatic advertising, joint controllership among AdTech intermediaries, and reliance on another party's consent mechanism.
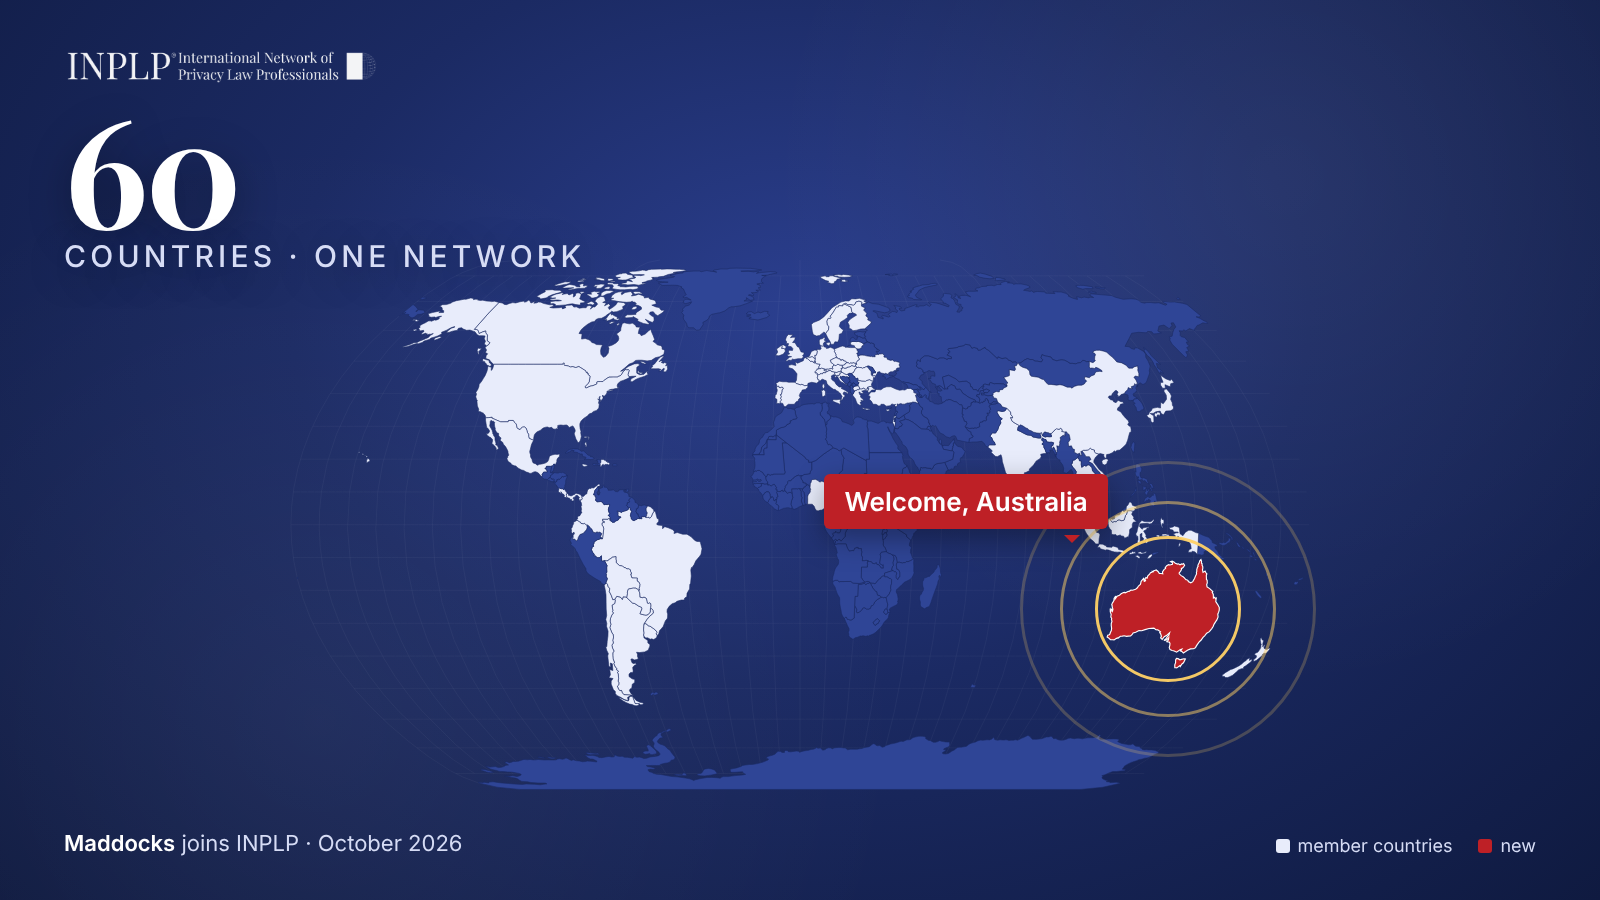
INPLP reaches 60 countries: a warm welcome to Maddocks, our first member in Australia
With Maddocks from Sydney, the International Network of Privacy Law Professionals welcomes its first member firm from Australia — and is now represented in 60 countries on six continents.
Ukraine joins INPLP: a warm welcome to Legal IT Group
With Legal IT Group from Kyiv, the International Network of Privacy Law Professionals welcomes its first member firm from Ukraine. INPLP is now represented in 59 countries.
A Review of the EDPB’s Anonymization Guidelines in Light of EDPS v SRB
When, and for whom, does information constitute personal data? The Court of Justice of the European Union (CJEU) addressed this question in EDPS v SRB (C-413/23 P). Its judgment clarified the treatment of pseudonymized data but prompted further debate over implementation. The Digital Omnibus proposal sought to amend the GDPR’s definition of personal data; the June 2026 compromise text removed that amendment and reassigned the proposed pseudonymization powers to the European Data Protection Board (EDPB). Against this background, the EDPB opened its draft Guidelines 02/2026 on Anonymization for consultation on 8 July 2026. The draft reflects much of the CJEU’s reasoning but, in our view, also extends beyond it. This article follows the dispute from the initial complaints through the judgment and the EDPB’s subsequent guidance.
Read, shred and forget? New Swedish case law and the manual-processing gap in the GDPR
Swedish employers routinely ask applicants and employees to show an extract from the criminal records register (belastningsregistret). Article 10 GDPR allows criminal conviction data to be processed only under official authority or where law authorises it, which most private employers lack. In AD 2026 nr 27 (case A 156/24), the Labour Court held that an employer who merely receives, reads and destroys such an extract falls outside the GDPR altogether.
